
Tech CEO Arrested in Russian-Software Concealment Case
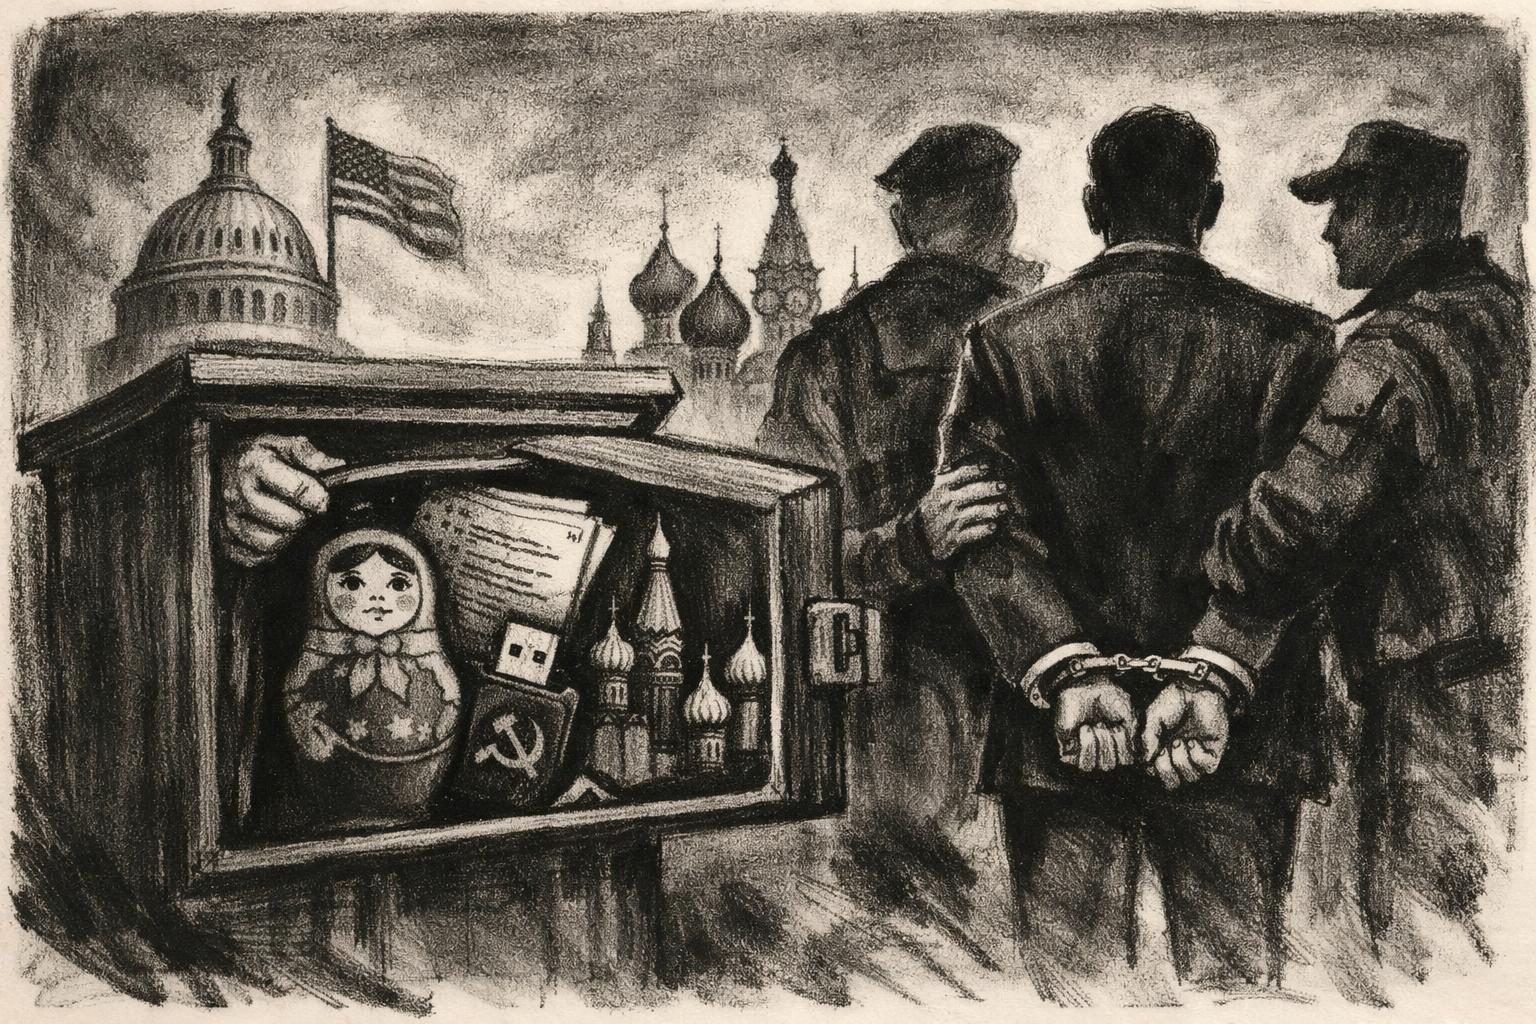
Federal prosecutors say the chief executive of a Virginia-based software company and a Russian national were arrested on a criminal complaint alleging that the company hid Russian ownership and Russian development ties while selling software to U.S. government agencies. According to the complaint, the business presented itself to federal customers in a way that obscured who actually controlled the company and where the product was being developed. Prosecutors say those claims were false and were made over a period of years, not in a one-off mistake or a simple contract dispute. The case, as described by federal authorities, is being treated as a criminal matter tied to procurement fraud and possible national-security risk, which is a much bigger problem than a vendor filing bad paperwork. That distinction matters because the government is not merely accusing the company of sloppiness; it is alleging an intentional effort to mislead federal buyers about the software’s provenance and the people behind it.
The allegations cut to a vulnerability that has been obvious for years but difficult to fully police: agencies increasingly rely on outside software for sensitive functions, yet they still often have to take vendors at their word when it comes to ownership, access, and development controls. If the complaint is correct, the government was purchasing tools under a false picture of who could touch the source code, who could influence updates, and whether a foreign nexus existed behind the scenes. That is the kind of supply-chain problem officials warn about in speeches and cybersecurity strategy documents, then struggle to catch before a product is already embedded in federal systems. It also illustrates how procurement fraud can overlap with national-security concerns without changing much in the day-to-day mechanics of the scheme; a false certification, a concealed relationship, and a handful of reassuring answers can be enough to get a product through the door. The complaint suggests prosecutors believe this was not an accidental omission but a deliberate concealment intended to preserve access to government business.
The arrest of the two defendants makes the case more immediate, but it also raises broader questions about how thoroughly agencies vet the software they buy and the companies that sell it. Federal purchasers often focus on functionality, price, delivery timelines, and security checkboxes, but those controls depend on honest disclosures from vendors and the ability to verify them when necessary. When a company is accused of masking foreign ownership or foreign development ties, the issue is not only whether the product worked as advertised, but whether the government ever had a real understanding of the risks it was accepting. That is why this complaint is likely to reverberate beyond the named company if prosecutors can substantiate their claims. Contracting officers, compliance teams, and agency lawyers may all be asked whether warning signs were missed, whether more diligence should have been required, and whether existing procurement rules are adequate to catch a vendor that is willing to lie about something as fundamental as control of the software supply chain.
The government’s posture in the case suggests it wants the allegations to be read as a warning, not just a standalone prosecution. By framing the matter as a conspiracy to deceive federal customers, prosecutors are signaling that the alleged conduct may have affected multiple agencies and may have involved coordinated misrepresentations rather than isolated statements made by mistake. That framing also gives the case symbolic weight at a time when Washington is already worried about foreign influence, data security, and the trustworthiness of vendors that touch public infrastructure. If the evidence shows the company knew about Russian ownership and development links while telling agencies the opposite, the case could become a model for more aggressive enforcement against software sellers that treat transparency as optional. If the government cannot prove that level of knowledge and intent, then the prosecution may still have exposed how weak the current system can be when it depends on vendor honesty instead of robust verification. Either way, the episode is likely to add fuel to demands for tighter software provenance rules, stronger screening for contractors that handle sensitive systems, and a less forgiving view of claims that sound clean on paper but cannot survive scrutiny.
Comments
Threaded replies, voting, and reports are live. New users still go through screening on their first approved comments.
Log in to comment
No comments yet. Be the first reasonably on-topic person here.